Free tool · Open source · MIT
Quantum Ready Labs: is your host ready for the quantum era?
Type a host name and in about a second Quantum Ready Labs opens a handful of TLS connections to it, as a browser would, and reports in plain language where the host stands on the post-quantum transition: a stage word, a score out of 100, what is urgent, what cannot be fixed yet, and the one next step.
Open quantumreadylabs.com Source on GitHubAPI documentation The Florida study
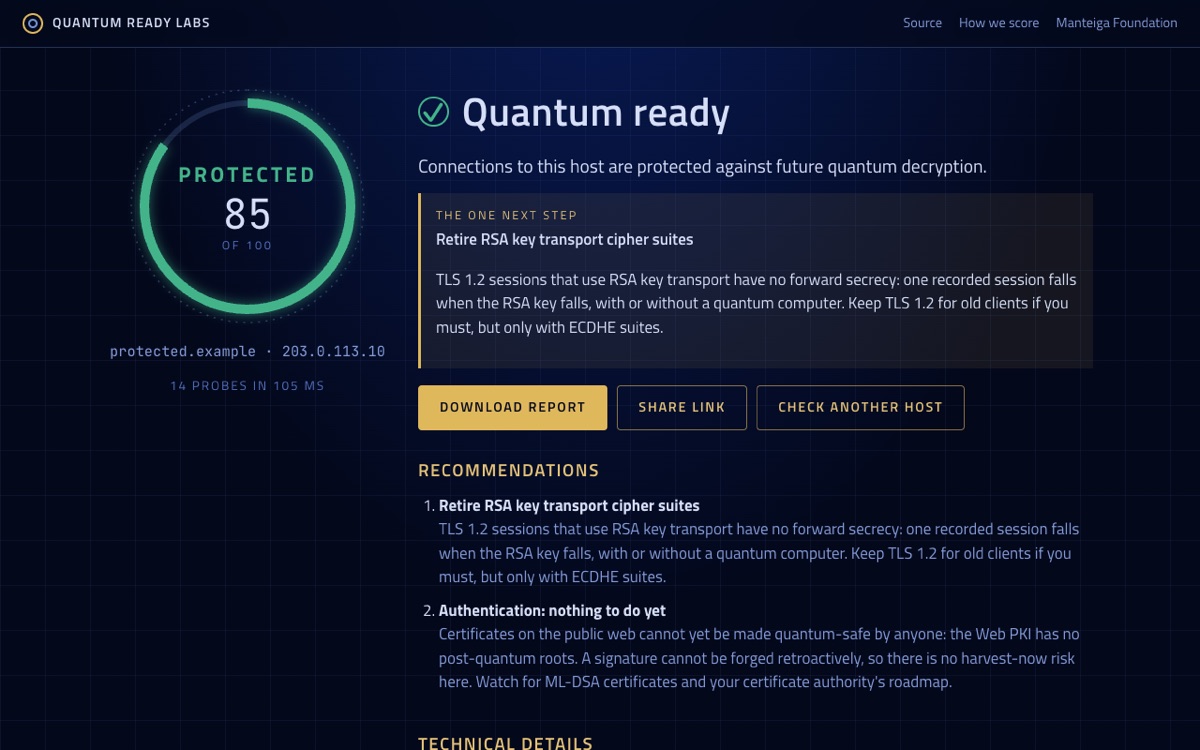
The threat it measures is "harvest now, decrypt later": encrypted traffic recorded today falls on the day a quantum computer able to break RSA and elliptic curves exists. That is a confidentiality problem, and it is solved in the key exchange, which is why browsers, OpenSSL and the large CDNs already negotiate hybrid post-quantum key exchange on every connection that supports it. Certificates are a different matter: a signature cannot be forged retroactively, and the public Web PKI has no post-quantum roots yet, so the report says so plainly and does not alarm about something nobody can act on today.
Four stages. Exposed: TLS 1.3 is not available, sessions can be recorded today and decrypted later. At risk: TLS 1.3 with forward secrecy but no post-quantum key exchange, safe today and harvestable. Protected: hybrid post-quantum key exchange (X25519MLKEM768 or equivalent) is accepted. Ready: protected, no legacy key transport, short-lived automated certificates. The score sits under the stage word; the rubric is published, and it measures quantum readiness only, without competing with the general TLS checkers.
The engine builds TLS ClientHello messages by hand and reads the server’s first reply in clear: offer one key-exchange group with no key share, and a supporting server answers with a HelloRetryRequest naming it, while a non-supporting server sends an alert. No post-quantum cryptography is implemented and no handshake completes, so the result is identical on every platform. Fourteen probes per scan, run concurrently, 20 to 500 ms per host. The result is a page that can be shared by link, in six languages, or downloaded as a print-ready PDF.
The API is open and needs no key: one GET answers with the finished scan, its share link and its PDF link in one JSON object; a POST streams the events the page draws from. Twenty scans per caller and six per host in any ten minutes; results under 24 hours come from cache. The same scanner runs in a terminal from the repository, and a study feature scans a named population on one day and publishes a state-of-readiness note: the first covered Florida’s 81 banks and credit unions and was reported by Quantum Zeitgeist and the Practical Commerce Chamber.
Screens
Taken from the tool itself, as it runs.
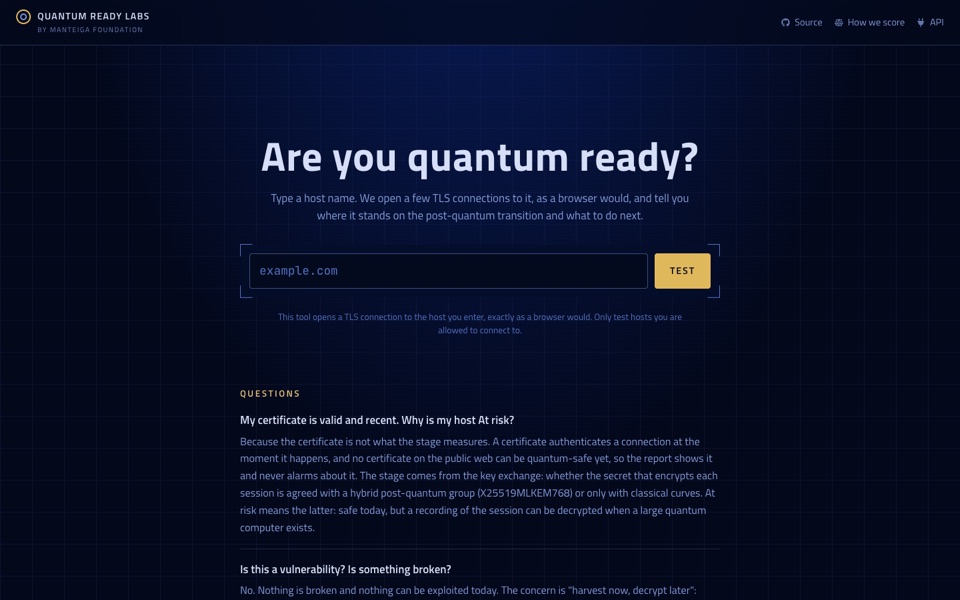 The question, one field: are you quantum ready?
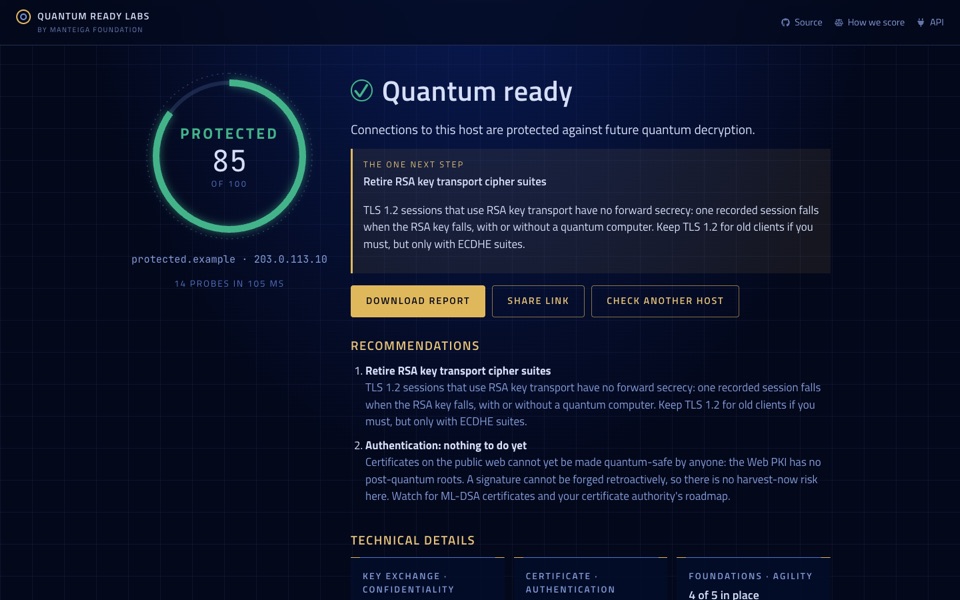 Protected, 85: hybrid post-quantum key exchange accepted
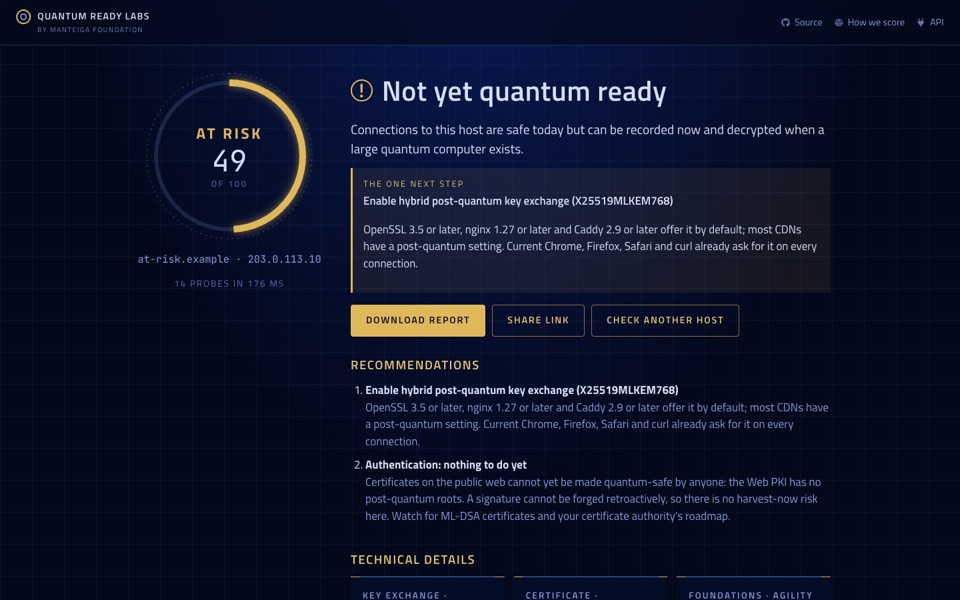 At risk, 49: TLS 1.3 without post-quantum key exchange
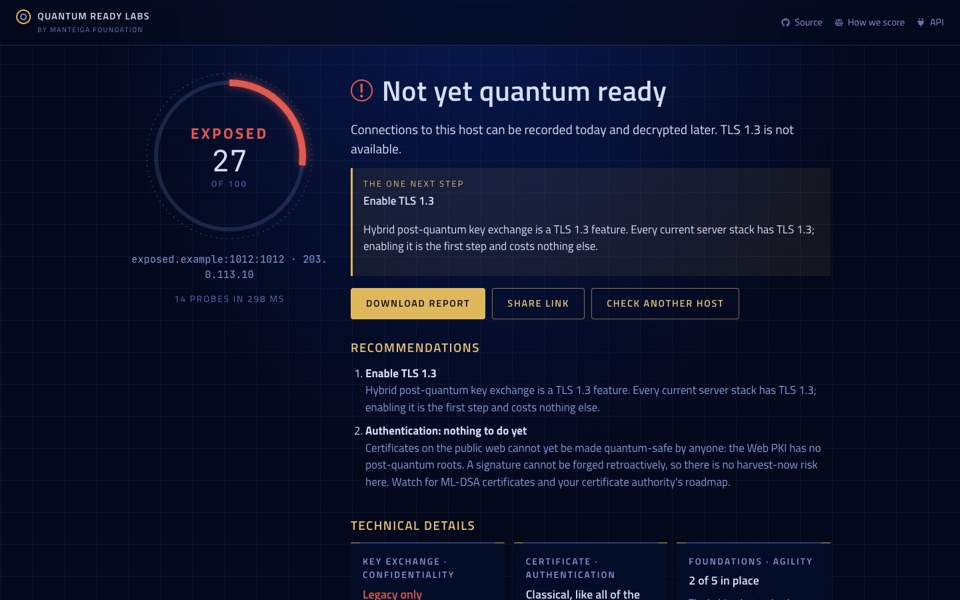 Exposed, 27: no TLS 1.3, the next step is to enable it
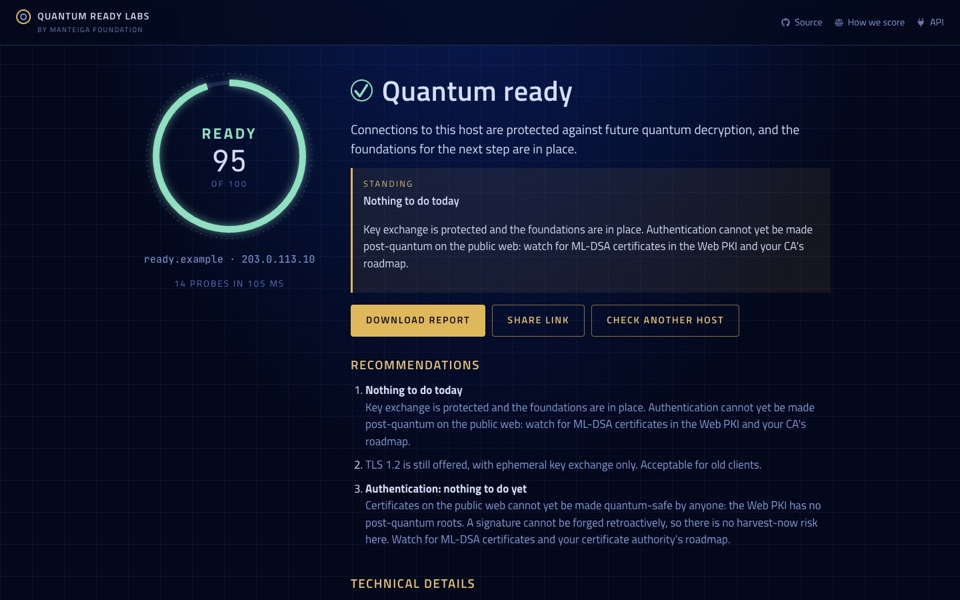 Ready, 95: nothing to do today
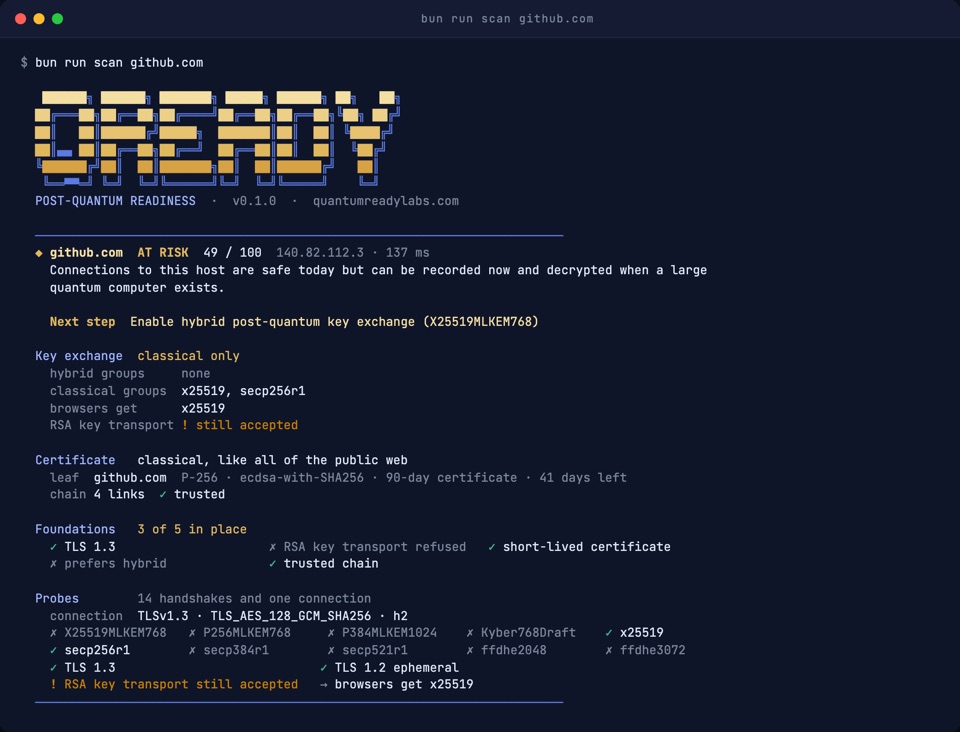 The same scan in a terminal: bun run scan github.com