Sample report · 28 pages · PDF
WISP Report to the Board of Directors: a sample report
The yearly Written Information Security Program report a bank’s board receives, delivered to a client and anonymized for sharing. Twenty-eight pages that account for a year of assessments, the maturity reached, the safeguards in place and what comes next, in the language a board reads.
A WISP report answers the board’s duty under data protection law: that the information security program exists, is executed, and is adjusted as risks change. This one covers a reporting year in which the bank commissioned twenty-one independent assessments: external and internal penetration tests in two rounds, denial-of-service tests, internal and external vulnerability assessments, a social engineering campaign, cloud and IT infrastructure risk assessments, tabletop exercises of the incident response plan, and third-party and SOC report reviews of a critical vendor.
Each assessment has its page: what was tested, the rating, the trend against earlier years drawn from the same tables, and the remediation plan the bank established. A cybersecurity maturity page states the consolidated score against a target on the NIST Cybersecurity Framework 2.0 categories; a page per CSF core function shows how the program adopts it. The report records that no technical security breach occurred in the year, lists the safeguards by critical area, reports the oversight of service providers, and closes with the conclusions and recommendations the firm gives the board.
The structure follows the program itself: risk identification and assessment, detecting and preventing attacks, responding to attacks, designing and implementing safeguards, overseeing service providers, and adjusting the program. A table of contents and an executive summary put the year on one page for directors who read nothing else.
In this edition the bank, its vendors, its application names, the people and the named statute are withheld; the assessments, ratings, counts and dates are as delivered, and the one capture is redacted. The report exists in English and Spanish. This is the shape of the governance reporting N30 delivers to boards in regulated sectors.
What is inside
- Executive summary: the year on one page, with the consolidated rating
- Introduction, scope and the components and goals of the program
- The year’s assessment program: 21 assessments with their ratings
- Penetration tests, denial-of-service tests and vulnerability assessments with multi-year trends
- Cybersecurity maturity on the NIST CSF 2.0 categories
- Social engineering, cloud, IT infrastructure and tabletop results
- Detecting, preventing and responding to attacks; safeguards; service providers
- NIST CSF 2.0 core functions, conclusions and recommendations, appendices
For boards, CISOs and information security officers in banks and other regulated organizations who report yearly on their program.
Pages from the report
8 of the 28 pages, as delivered. The PDF has them all.
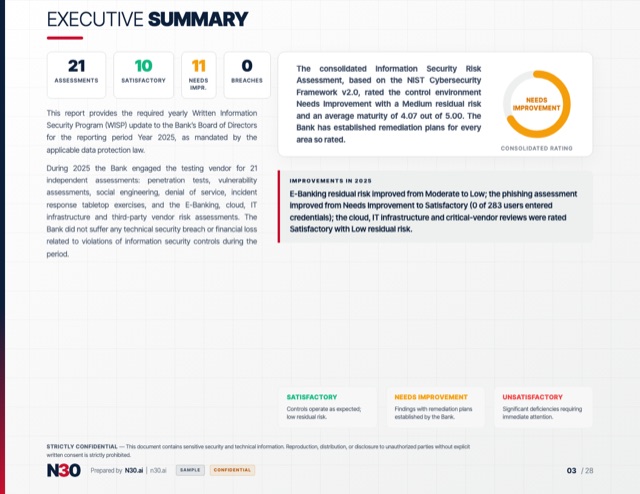 03 Executive summary: the year on one page
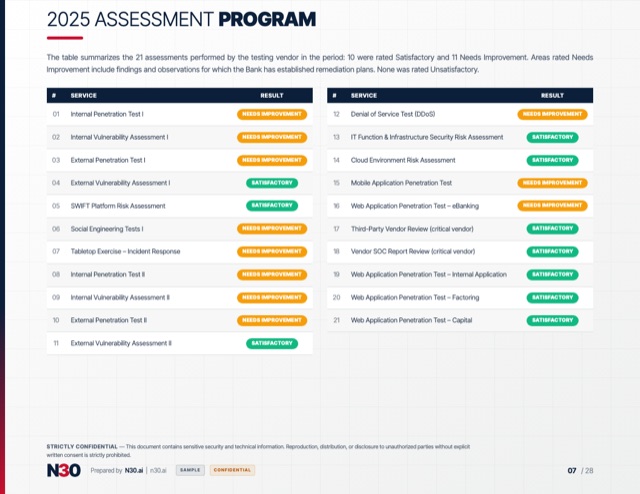 07 The assessment program: 21 assessments rated
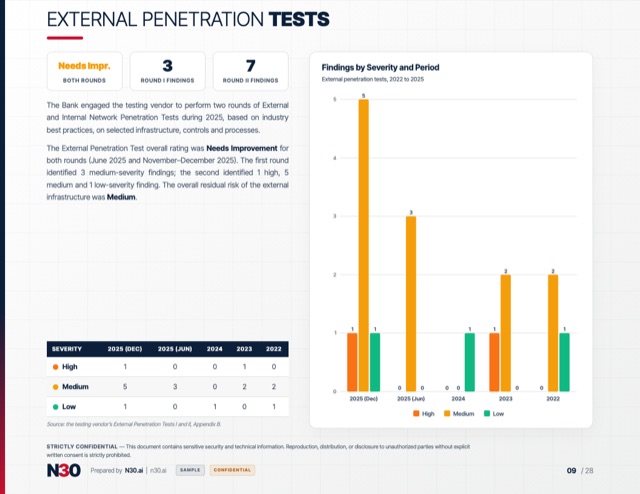 09 External penetration tests, the trend
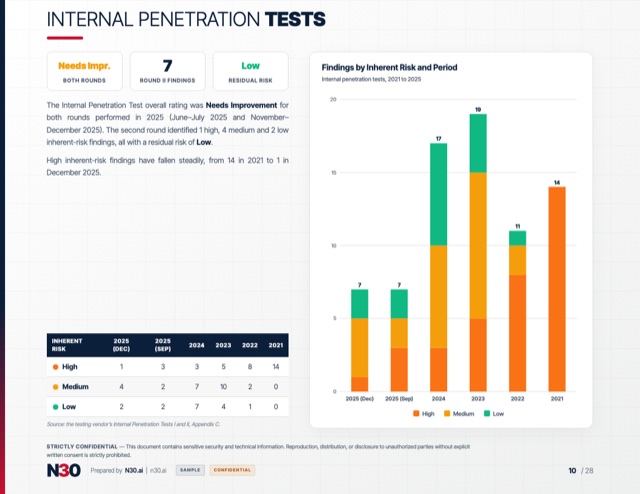 10 Internal penetration tests, the trend
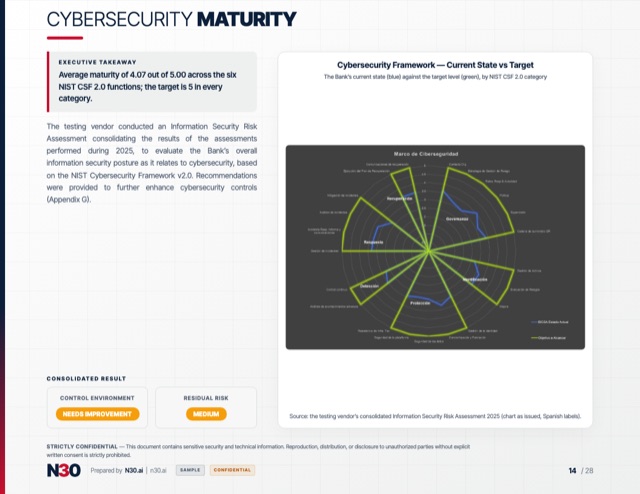 14 Cybersecurity maturity against the target
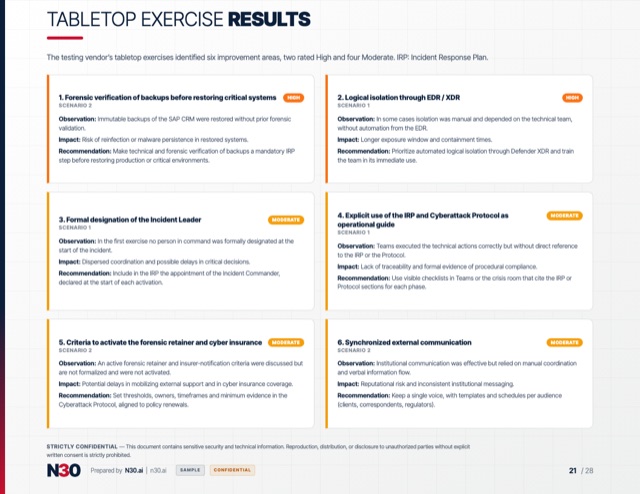 21 Tabletop exercise results
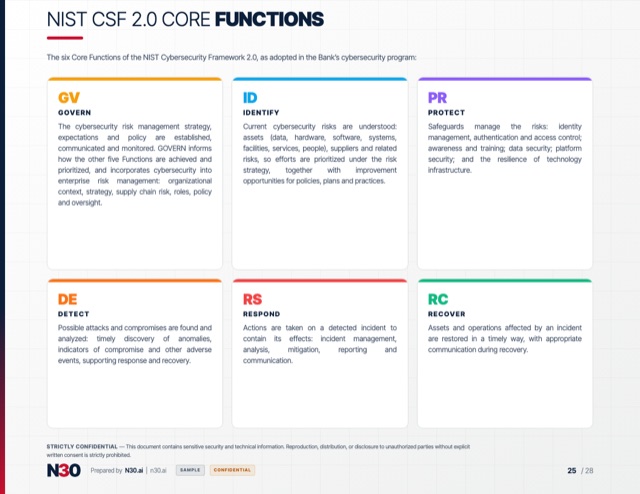 25 NIST CSF 2.0 core functions
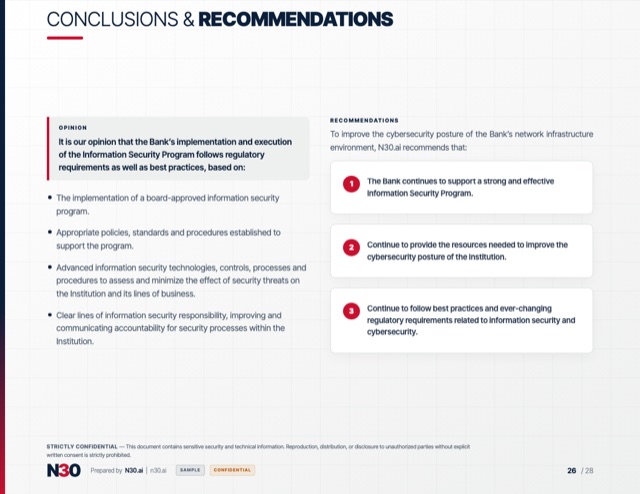 26 Conclusions and recommendations to the board