Sample report · 42 pages · PDF
Azure Baseline Cloud Security Assessment: a sample report
A baseline configuration review of an Azure and Microsoft Entra tenant, delivered to a client and anonymized for sharing. Forty-two pages: the scorecard, the findings with their evidence, and the roadmap, exactly as the client received them.
The engagement reviewed a Microsoft Azure estate of two dozen subscriptions and its Entra directory with read-only roles, against the customer-side domains of the Cloud Security Alliance Cloud Controls Matrix (CCM v4): identity and access management, logging and monitoring, data security and encryption, and infrastructure security. Forty-seven checks were assessed from configuration data exported through the Azure portal and the command line, each mapped to the CCM control it evidences, and each rated pass, fail or partial with the export that proves it.
The report opens with an executive summary and a control treemap that shows every assessed control sized by the checks behind it and coloured by its score, so a board or a CIO can see at a glance where the tenant stands. Three scorecard pages list the checks domain by domain. Eighteen findings follow, two High, ten Medium and six Low, ordered by severity: each finding states the exposure, the resources concerned, the CCM control, the remediation and the effort, and where a capture was taken an evidence page shows the portal view and the validation steps. A 30/60/90-day roadmap closes the report, Critical and High items in the first month.
Severity is rated by exposure and blast radius, never by a tool score: a detection gap rates below an exposure of the same reach, and two findings that describe the same blind spot are not both rated High. Resource names, tenant and subscription identifiers, people and the managed-detection provider are withheld in this edition; the figures and the ratings are as delivered. The captures carry navy boxes where the client was identifiable.
This is the shape of every cloud assessment N30 delivers, on Azure, AWS or Google Cloud: a scorecard the client can re-measure, findings with evidence a reviewer can verify, and a roadmap that fits a quarter. The instruments behind it are open source.
What is inside
- Executive summary with the posture by domain
- CSA CCM v4 control treemap: every assessed control by score
- Scope, method and the read-only access used
- Baseline scorecard: 47 checks across IAM, logging, data protection and infrastructure
- Findings overview and 18 findings with severity, CCM control, resources, remediation and effort
- Evidence pages with redacted portal captures and validation steps
- 30/60/90-day remediation roadmap
For CIOs, CISOs and cloud teams who want to see what a configuration review returns before commissioning one.
Pages from the report
8 of the 42 pages, as delivered. The PDF has them all.
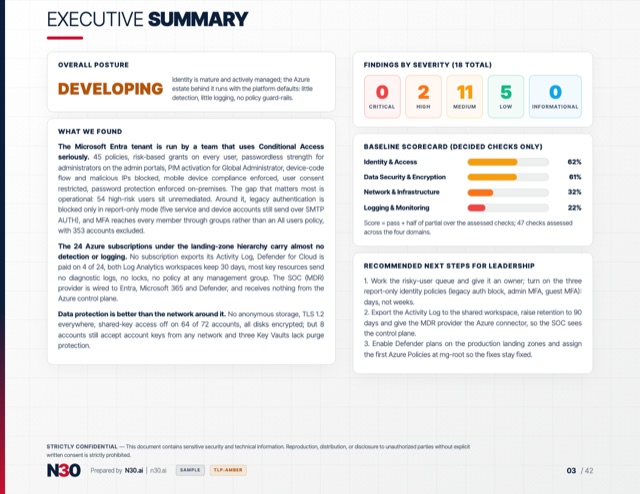 03 Executive summary: the posture in one page
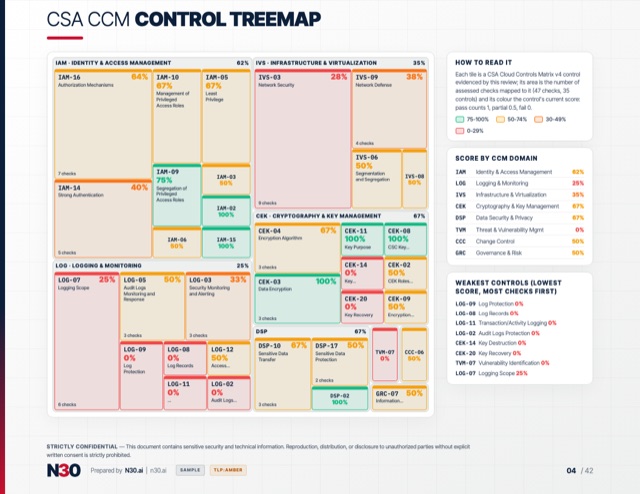 04 The CSA CCM control treemap
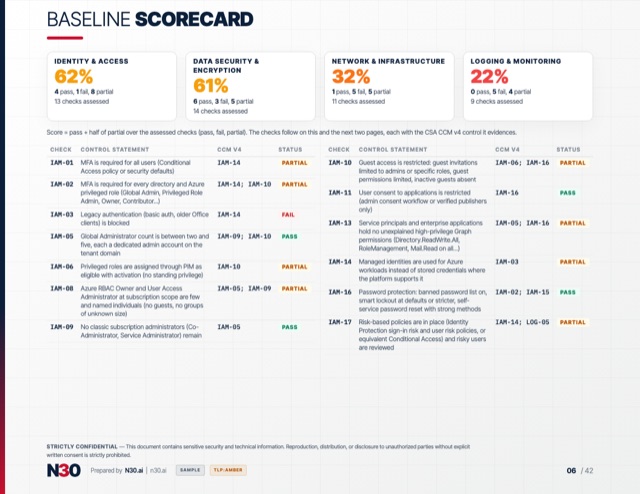 06 Baseline scorecard, identity and access
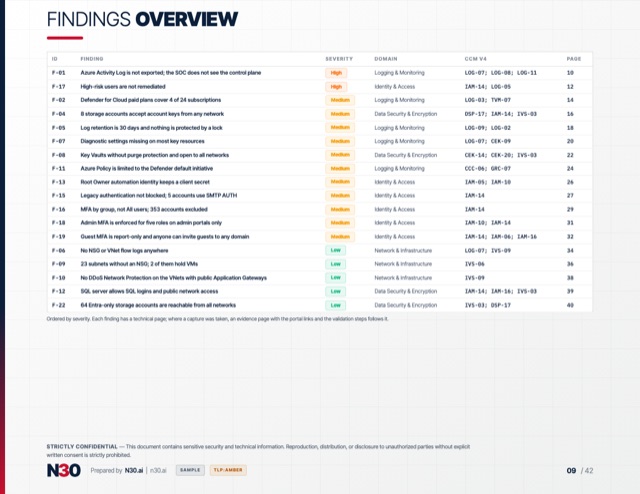 09 Findings overview, ordered by severity
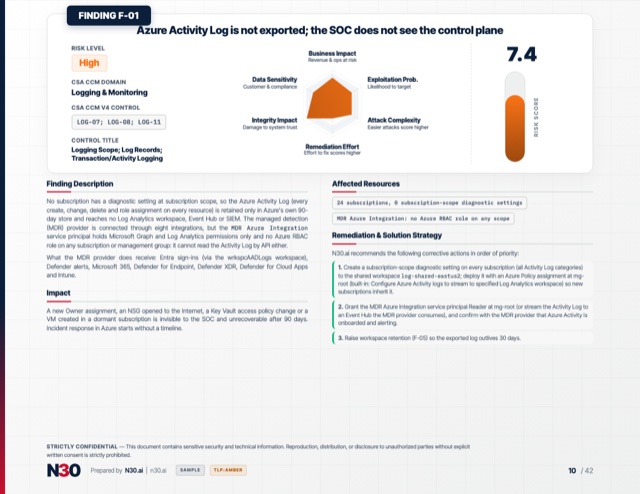 10 A finding: exposure, control, remediation, effort
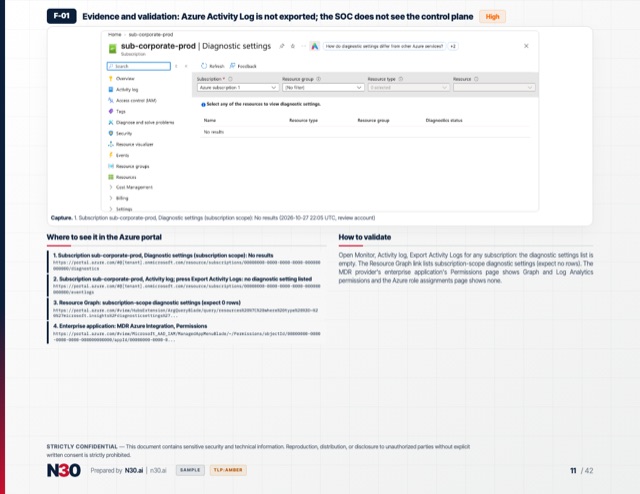 11 Its evidence page, the capture redacted
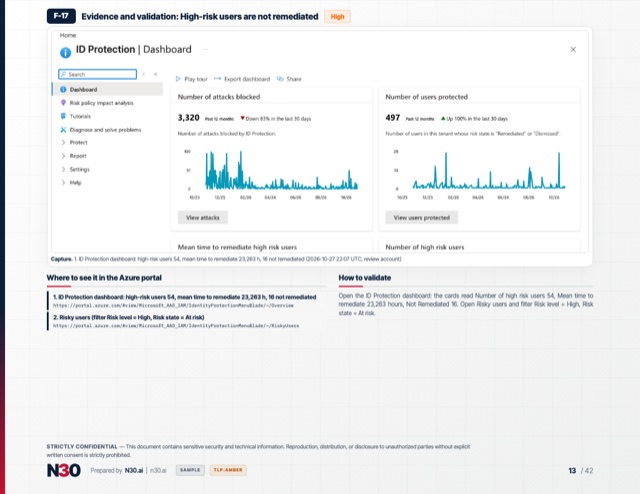 13 Evidence for the high-risk users finding
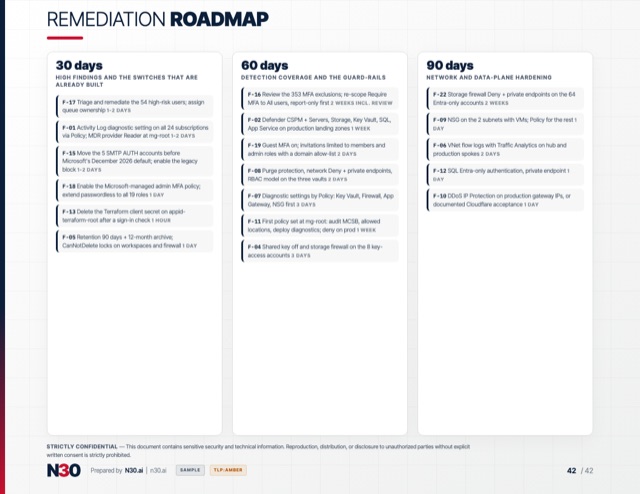 42 The 30/60/90-day roadmap